
Unified AI Governance Architecture
Most companies did not plan their AI governance. It just sort of accumulated. One team wrote a policy document. Another kept a spreadsheet of approved tools. Legal had opinions, security had a checklist, and somewhere in the middle a chatbot went live that nobody officially signed off on. Sound familiar?
That scattered approach works, barely, when a company uses two or three AI tools. It falls apart when every department is experimenting and vendors keep adding AI features to products you already own. This is where the idea of a unified AI governance architecture comes in — one connected structure instead of a pile of separate rules. If you are still getting oriented, it helps to understand the different types of AI a company might use, because each type brings its own risks and needs its own level of oversight.
In short: A unified AI governance architecture is a single, connected framework that ties together an inventory of every AI system in use, the policies that govern them, risk assessments, approval steps, ongoing monitoring, human oversight, and audit records — so nothing runs unnoticed and every decision can be traced back to a person and a rule.
What Is a Unified AI Governance Architecture
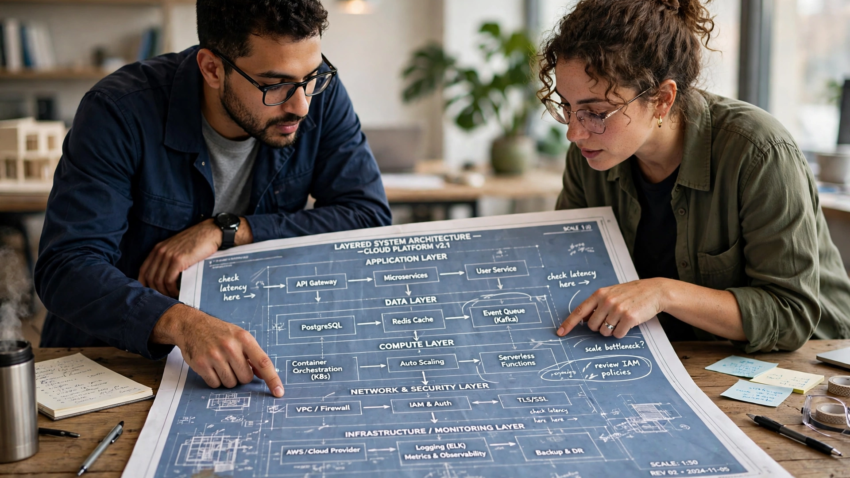
Think of it like the blueprint of a building. A building has a foundation, a frame, plumbing, wiring, and safety systems. Each part does a different job, but they are designed together, and a change in one place is checked against the rest. Governance works the same way. The “architecture” is not one tool or one document — it is the way the pieces connect.
In a unified setup, the inventory knows which systems exist. The policies say what is allowed. The risk process decides how much scrutiny each system deserves. Approvals happen before launch, not after an incident. Monitoring watches systems while they run, and audit trails record what happened so questions can be answered later. When those pieces share the same data and definitions, governance stops being a paperwork exercise and starts working like an actual system. This layering is similar in spirit to the 3 pillars of AI platform architecture, where structure is what keeps powerful technology manageable.
“Unified” is the word that matters. Plenty of companies own all the individual pieces. What they lack is the connection between them — the policy that never reaches the procurement team, the approval that lives in an email thread nobody can find six months later.
Why Companies Move From Scattered Rules to One Structure
The push usually starts with an uncomfortable question. A board member asks how many AI systems the company is running. A regulator asks for evidence. A customer asks how their data is handled. And nobody can answer with confidence, because the information lives in twelve different places — or nowhere at all.
There is also a simpler reason: scattered governance is slow. Every new tool triggers the same debates from scratch. Teams wait weeks for answers that should take days, so they route around the process, which creates exactly the shadow AI the process was meant to prevent. Many leaders eventually realize that AI transformation is a problem of governance far more than it is a problem of technology. The models work fine. The management structure around them is what breaks. For the challenges and solutions, see Ai transformation is a problem of governance.
A unified architecture fixes the boring problems first. One place to look. One vocabulary. One path from “someone has an idea” to “this system is approved, monitored, and accounted for.” Speed and control stop being enemies, because a clear process with fast lanes for low-risk tools is quicker than chaos with good intentions.
The Layers of a Unified AI Governance Architecture
Every architecture looks a little different depending on the company, but most unified designs share the same core layers. Here is how they fit together, and what goes wrong when one is missing.
| Layer / Component | What It Does | What Happens Without It |
|---|---|---|
| AI inventory and registry | Keeps one live list of every AI system, model, and tool in use, who owns it, and what data it touches | Shadow AI spreads; nobody knows what is running or where company data is going |
| Policy layer | Defines the rules — acceptable use, data limits, prohibited uses, and standards systems must meet | Each team invents its own rules, and enforcement becomes an argument instead of a check |
| Risk assessment | Scores each system by impact and likelihood of harm, so scrutiny matches the stakes | A trivia chatbot and a hiring tool get the same review — or the hiring tool gets none at all |
| Approval workflows | Routes systems through the right sign-offs before launch, scaled to their risk level | Tools go live on a manager’s say-so, and problems surface only after real damage is done |
| Monitoring and drift checks | Watches live systems for errors, bias, performance decay, and behavior drifting from what was approved | A system that was safe at launch quietly degrades, and nobody notices for months |
| Human oversight points | Builds in named people who review outputs, handle exceptions, and can pause or shut a system down | Automated decisions run unchecked, and accountability dissolves into “the model did it” |
| Audit trails and reporting | Records decisions, approvals, changes, and incidents in a form that can be shown to leadership or regulators | When something goes wrong, there is no evidence of who approved what, or why |
Notice how the layers depend on each other. Risk assessment is useless if the inventory is incomplete, because you cannot assess systems you do not know exist. Monitoring is weak if approval never recorded what “good” was supposed to look like. And none of these layers is exotic — most companies have some version of each. The architecture is what you get when they stop being separate efforts and start feeding each other.
The Inventory Comes First
If there is a foundation layer, it is the registry. Every other control assumes you know what you are governing. Building the inventory usually starts with a sweep — procurement records, vendor contracts, and honest conversations with teams about what they are actually using. Keeping it alive matters more than building it once, which is why mature setups tie the registry to purchasing and IT processes, so a new tool entering the building enters the list automatically.
Policies People Can Actually Follow
The policy layer fails in a predictable way: a forty-page document in legal language that employees never read. Unified architectures work better with tiered policies — a short set of hard rules everyone knows (never paste customer data into unapproved tools, for example), plus detailed standards that apply by risk tier. And a rule that cannot be checked inside the approval process is just a hope.
How the Pieces Work Together in Practice
Walk through a simple example. A marketing team wants to adopt an AI writing assistant. In a scattered setup, someone buys it with a credit card and the company finds out later. In a unified architecture, the request enters the registry as a proposed system. The policy layer flags what data the tool may and may not receive, and risk assessment rates it — probably low to moderate, since it drafts public copy but could touch customer information.
Because the risk is moderate, the approval workflow is light: a standard review, confirmation that the vendor meets baseline requirements, and a named owner. After launch, monitoring checks that the tool is being used as approved, and the audit trail holds the whole story — who asked, who approved, under which rules. Now compare that with a system that screens job applicants. Same architecture, very different path: deeper assessment, bias testing, stricter oversight, a human reviewing outcomes, heavier documentation. One structure, proportionate responses. That proportionality is the whole point.
Events in the wider industry keep reminding companies why this matters. Reading about an AI governance wake-up call in the news is a lot less painful than living through one yourself.
Human Oversight and Accountability
Technology layers get most of the attention, but the architecture only works because people sit at defined points inside it. Oversight is not a suggestion box; it is a set of named roles with real authority. Someone owns each system. Someone can approve exceptions. Someone can pull the plug.
Good designs are specific about where humans stay in the loop — reviewing high-impact outputs before they reach a customer, checking a sample of automated decisions on a schedule, handling the cases the system flags as uncertain. They also plan for disagreement: when a business team wants speed and a reviewer wants caution, the architecture should say whose call it is. Accountability written into the structure survives deadline pressure; accountability that depends on goodwill does not.
How Real Frameworks Fit Into the Picture
A unified architecture does not have to be invented from a blank page. Well-known frameworks offer ready-made vocabulary and structure. The NIST AI Risk Management Framework, for instance, organizes governance around functions like governing, mapping, measuring, and managing AI risk — language many companies borrow when designing their layers. Regulation plays a role too: the EU AI Act classifies AI systems by risk and attaches obligations to each level, which maps naturally onto the risk-tiering approach described above.
The sensible way to use these frameworks is as scaffolding, not scripture. Take the risk categories, the documentation habits, and the oversight expectations, then shape them into an architecture that matches your size and your actual systems. A fifty-person company does not need the same machinery as a global bank — but the same layers, scaled down, still apply. For a regulated-sector example, see Leading Banks in Responsible AI and Governance.
Frequently Asked Questions
It is one connected structure for managing every AI system a company uses. Instead of separate policies, spreadsheets, and approval emails scattered across teams, it links an AI inventory, rules, risk checks, approvals, monitoring, human oversight, and audit records into a single framework, so each part supports the others and nothing falls through the cracks.
An AI policy is one layer — it states the rules. A unified AI governance architecture is the whole system that makes those rules real: the registry that shows what exists, the risk process that decides how much scrutiny each system gets, the approvals that happen before launch, and the monitoring and records that prove the rules were followed. A policy without the surrounding structure is mostly a statement of intent.
The core components are a central AI inventory or registry, a policy layer, risk assessment, approval workflows, monitoring and drift checks, defined human oversight points, and audit trails with reporting. Some companies add vendor management and incident response as their own layers, but those seven cover the essentials for most organizations.
Yes, but scaled to size. A small company might keep its registry in a single maintained document, use a short policy, and run approvals through one named person. What matters is that the pieces exist, connect to each other, and have owners. Small companies often benefit most, because building the structure early is far easier than untangling scattered AI use later.
Each AI system is assessed for the harm it could cause if it failed or behaved badly — considering the data it uses, the decisions it influences, and who is affected. Low-risk systems move through light, fast approvals with basic monitoring. High-risk systems, such as those affecting hiring, credit, health, or safety, get deeper assessment, testing, human review, and stricter documentation. The tier decides the treatment, which keeps governance proportionate instead of one-size-fits-all.
Yes, and most companies do exactly that. The NIST AI Risk Management Framework provides a structure for governing and managing AI risk that maps well onto the layers of an architecture, while the EU AI Act’s risk-based categories offer a model for tiering systems and attaching duties to each tier. Companies typically borrow the concepts and vocabulary, then adapt them into an internal architecture that fits their own size, industry, and systems.

Hamad Arshad writes and edits AI Next Top from Rahim Yar Khan, Pakistan. He has worked in SEO and digital marketing for over 7 years and started this site to explain AI tools and news in plain language for non-technical readers. Every guide here is checked against the real tool before it is published.
Leave a Reply